Continuous software delivery assurance
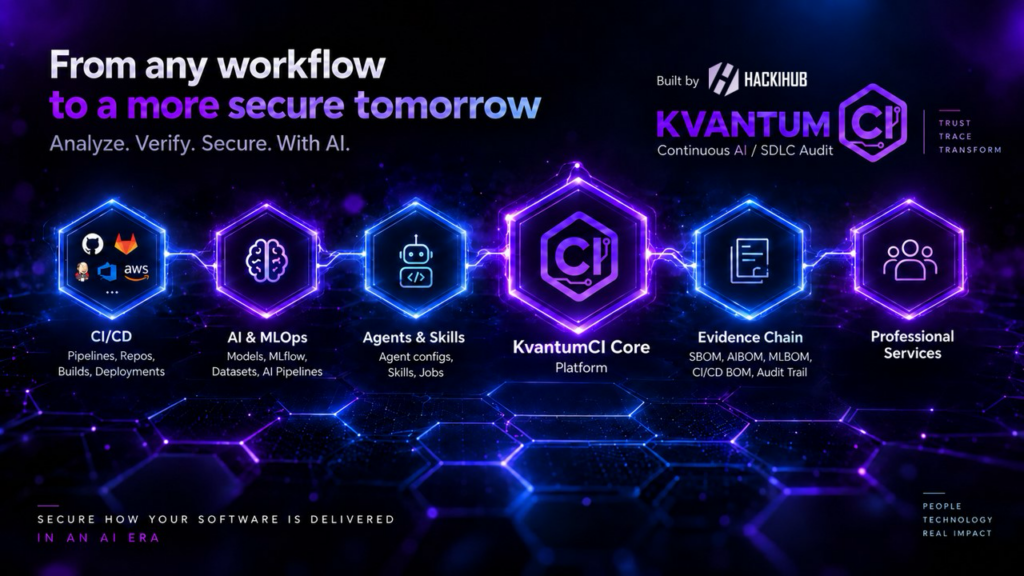
KvantumCI verifies whether the right engineering and security controls exist in your delivery workflows and how they’re configured. It runs continuously, not as a point-in-time audit, so posture stays current as your pipelines, repos, and teams change. OmniBOM consolidates the supply-chain evidence that comes out of that verification into one place.
What KvantumCI does
KvantumCI continuously verifies how software actually gets delivered — not what’s in your code, but whether the right controls exist around it and how they’re wired in.
- Discover: Map repositories, branches, jobs, and pipeline configuration signals across your estate.
- Detect: Identify missing, weak, or inconsistently applied controls in the path to production.
- Score & prioritize: Rank findings by what actually matters, not raw count.
- Guide remediation: Explain findings with pipeline context, not just a red flag.
- Re-verify: Confirm the fix held after changes ship.
It doesn’t replace SAST, SCA, container, or cloud runtime scanners. Those find issues in code, dependencies, and runtime. KvantumCI checks whether the right controls exist and are correctly wired into how that code gets delivered.
OmniBom
Every delivery pipeline produces evidence: dependencies, cryptographic assets, AI models, training data. But it’s usually scattered across a dozen disconnected tools and one-off exports that go stale the moment they’re generated. OmniBOM consolidates it into a single, continuously updated evidence layer inside KvantumCI.
- SBOM: Software bill of materials: every library and dependency in your codebase, tracked as it changes.
- CBOM: Cryptographic bill of materials: the algorithms, keys, and crypto assets your software actually relies on.
- AIBOM: AI bill of materials: the models, prompts, and AI pipelines wired into your delivery workflows.
- MLBOM: ML bill of materials: training data, model versions, and the pipeline components that produced them.
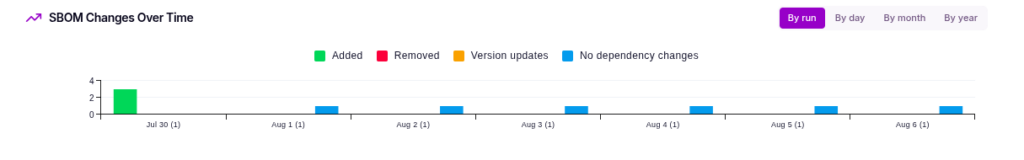
OmniBOM builds a timeline, not a snapshot. Every verification run adds to the evidence trail, so you can see how your software’s composition changed over time, not just what it looks like today. That matters when a customer asks “prove this hasn’t changed since the last audit,” or when an incident response team needs to know exactly what was running three weeks ago.
Works with the systems you already run
KvantumCI connects to the CI/CD ecosystems you’re already running rather than asking you to change how your teams ship. It reads pipeline configuration, repository structure, and job history from your existing source and CI systems to build its verification picture.